Selected work.
A sample of platforms and products we've designed and built. Most client engagements are under NDA. Ask us for more in a call.
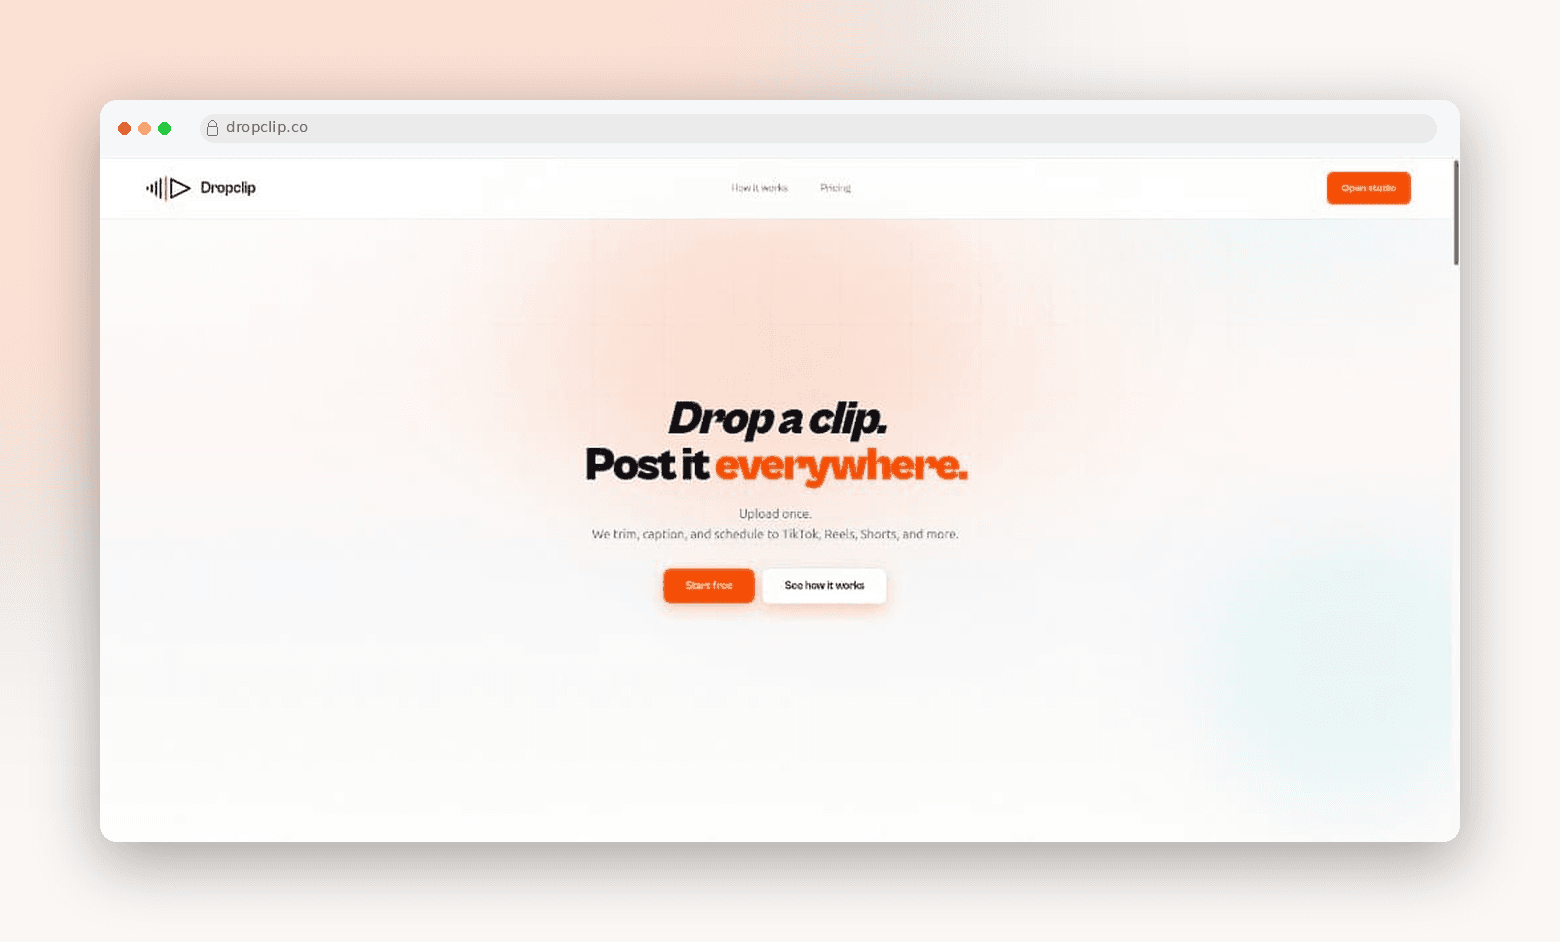
Dropclip
A creator platform for turning raw clips into social-ready posts. We designed and built the marketing site and the studio: timeline editing, styled captions, multi-track audio, and export to TikTok, Instagram, YouTube, X, and Facebook.
Security review
CybersecurityThe studio handles raw footage, captions, and tokens for every social account a creator connects. We reviewed the servers, the application, and the export path before it went live.
Server review
Hosts, services, and what is reachable from the public internet. Patching, SSH, and the jobs that move media — checked so a render box is not an open door.
Auth & accounts
Session handling, account recovery, and who can touch a project. Creators should not be able to see anyone else's clips or captions.
Media pipeline
Upload, storage, and export reviewed for access controls. Raw files and renders stay behind signed paths, not guessable URLs.
Third-party tokens
TikTok, Instagram, YouTube, X, and Facebook credentials stored and rotated so a leak in one place does not hand over the rest.
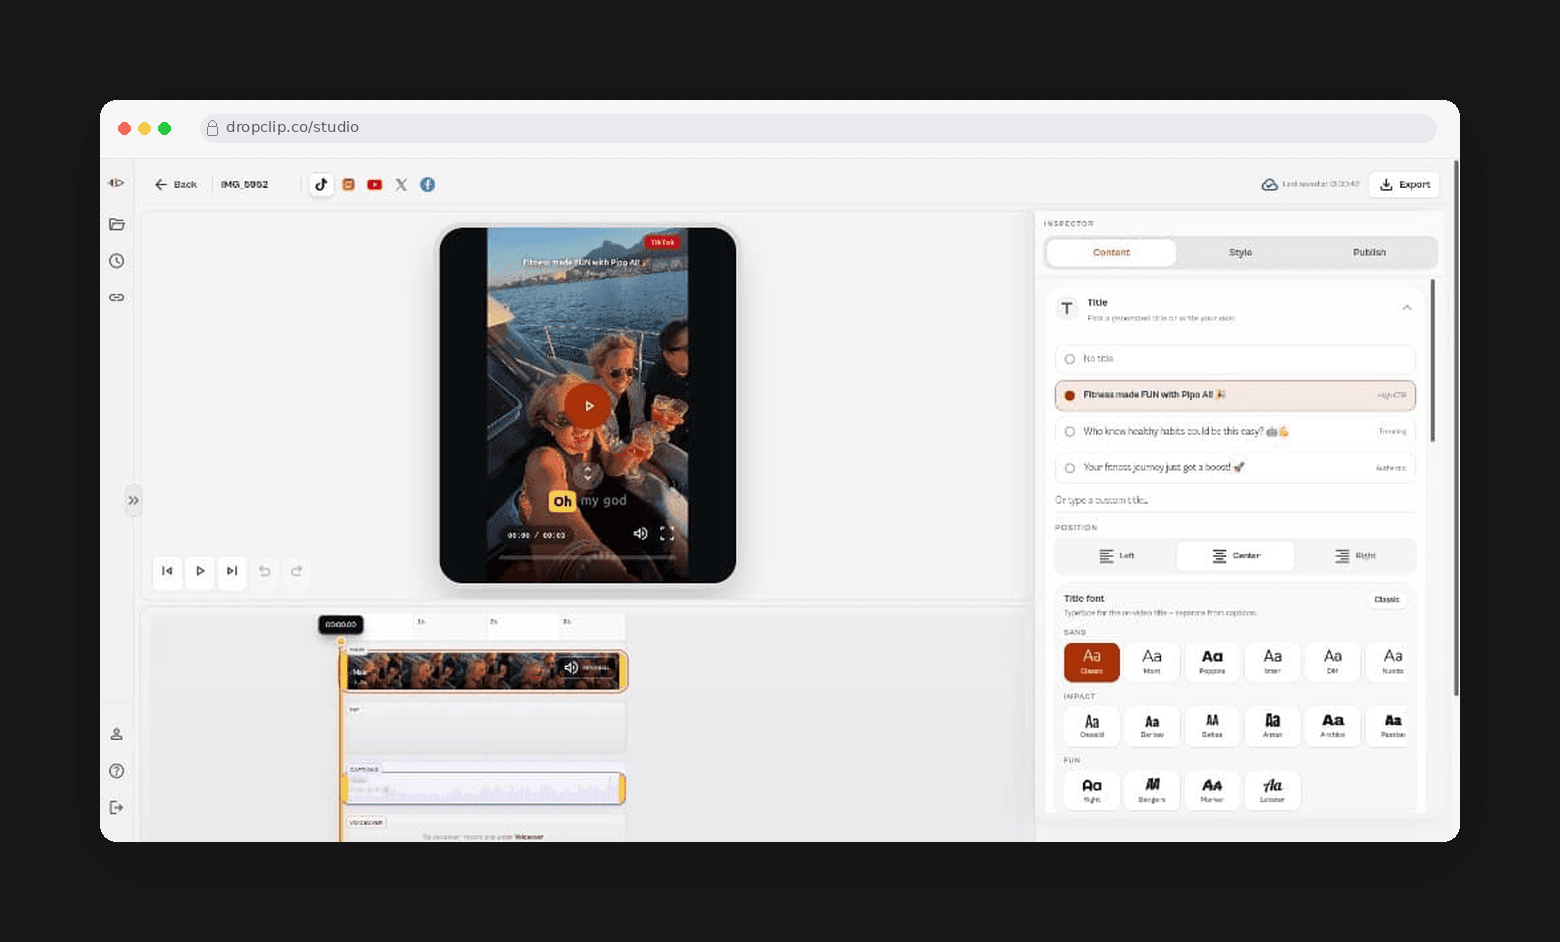
One upload path from raw clip to captioned, platform-ready posts, without a separate editor or scheduler.
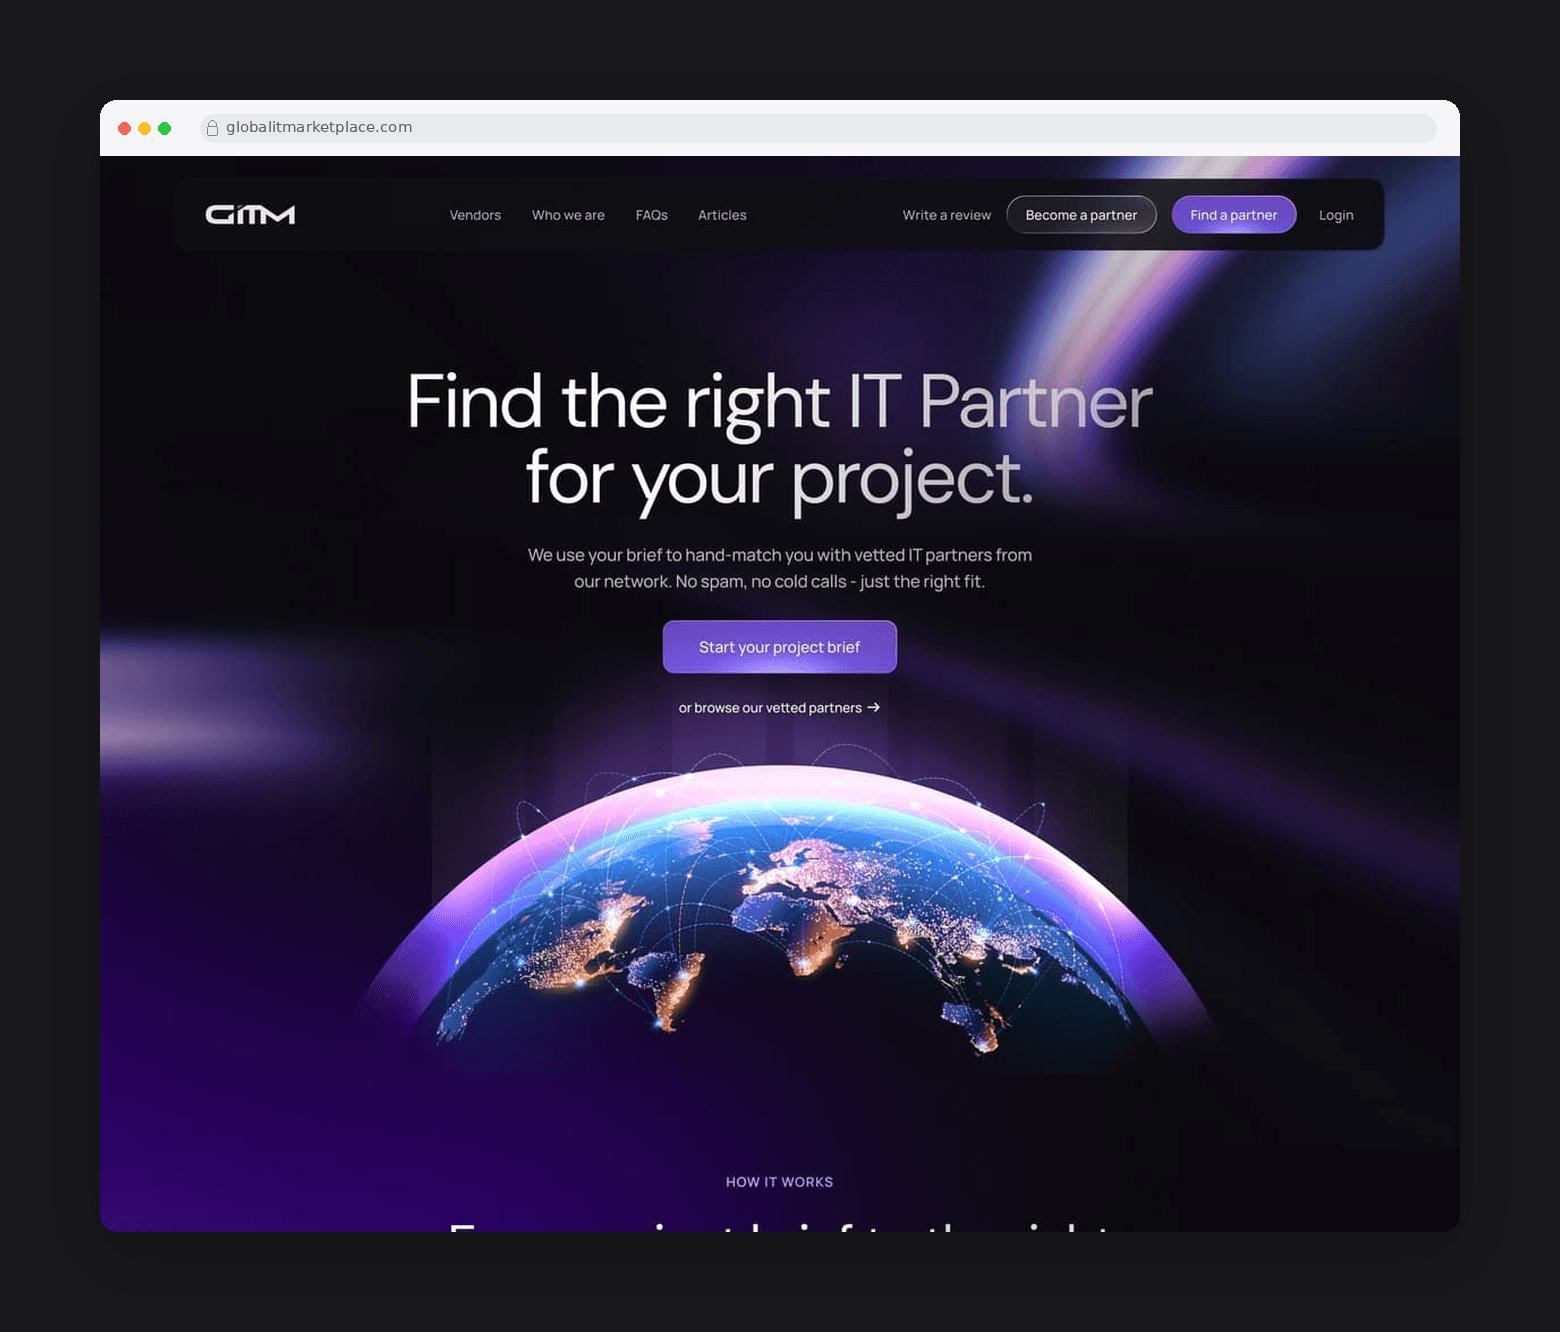
Global IT Marketplace
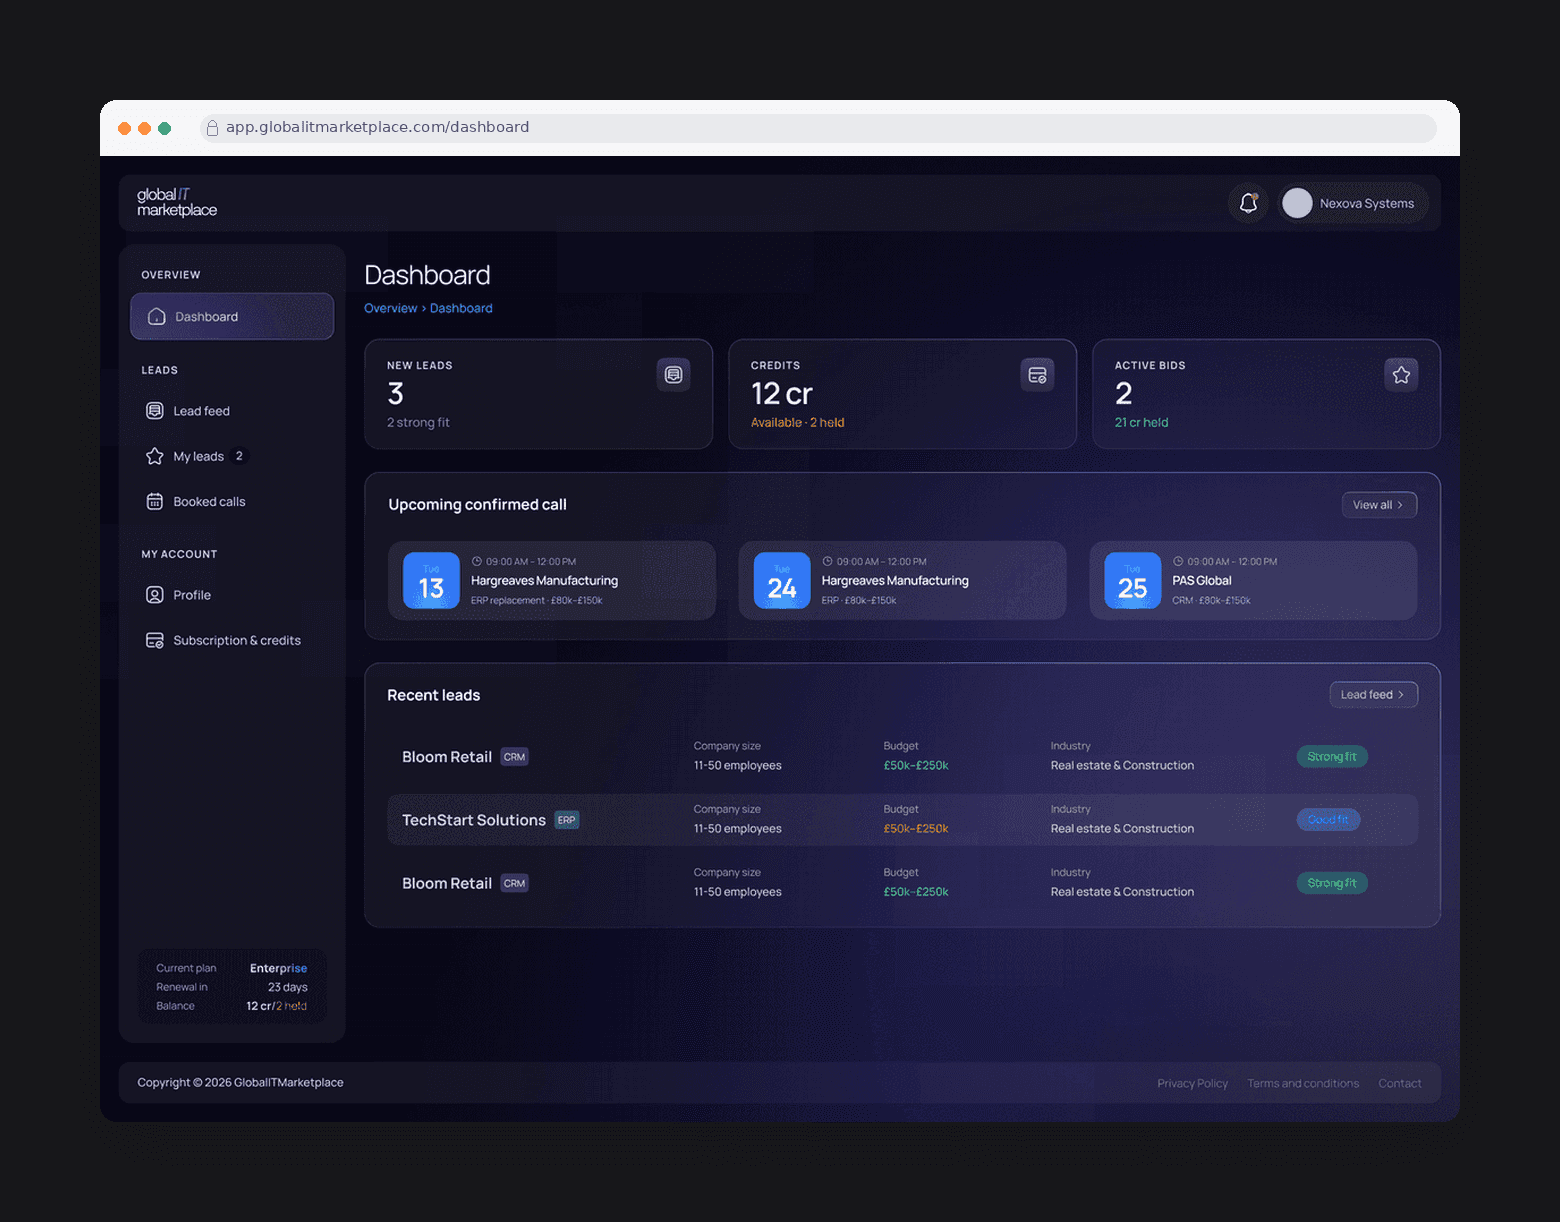
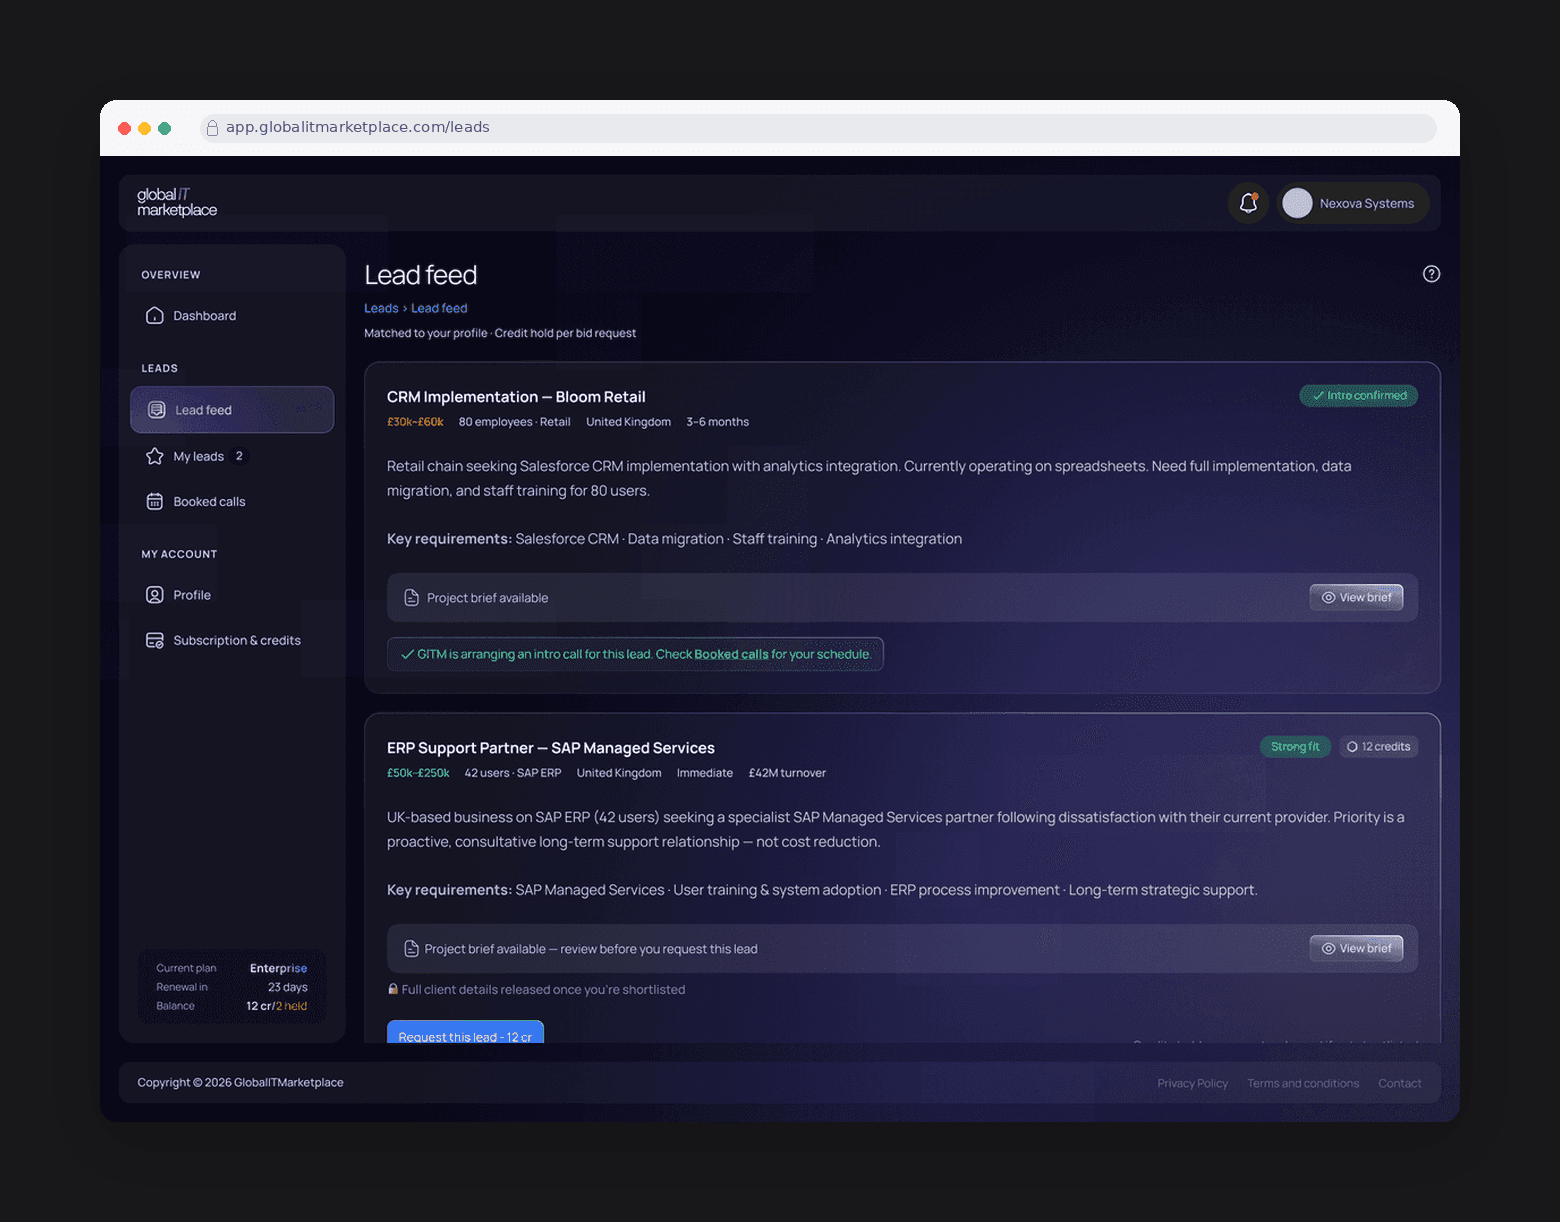
A two-sided marketplace connecting businesses submitting project briefs with vetted IT partners. We designed and built the public marketing site alongside the subscriber-facing dashboard: lead feed, credit-based bidding, booked calls, and account management. Before go-live we ran a full server review of the marketplace stack.
Security review
CybersecurityGITM sits on live project briefs, partner accounts, and a credit-based bidding system. We treated the servers as part of the product: reviewed, hardened, and documented before partners were invited in.
Full server review
Every host in the marketplace stack: OS, services, open ports, SSH, firewalls, and patch state. Anything that did not need to face the internet was taken off it. What remained was documented so the next change is not guesswork.
Identity & access
Business and partner roles, dashboard sessions, and who can bid, book, or see a brief. Least privilege on the servers as well as in the app — including how access is revoked when a partner leaves.
Data & lead isolation
Project briefs, partner profiles, and bidding history scoped so one subscriber cannot read another. Credits and booked calls checked against the same boundary.
Hardening & monitoring
Baseline hardening on the servers, TLS, backups, and the alerts that matter: failed auth, unexpected process or port changes, and the dashboard API misbehaving. A short incident path for the people who run it.
Fromo
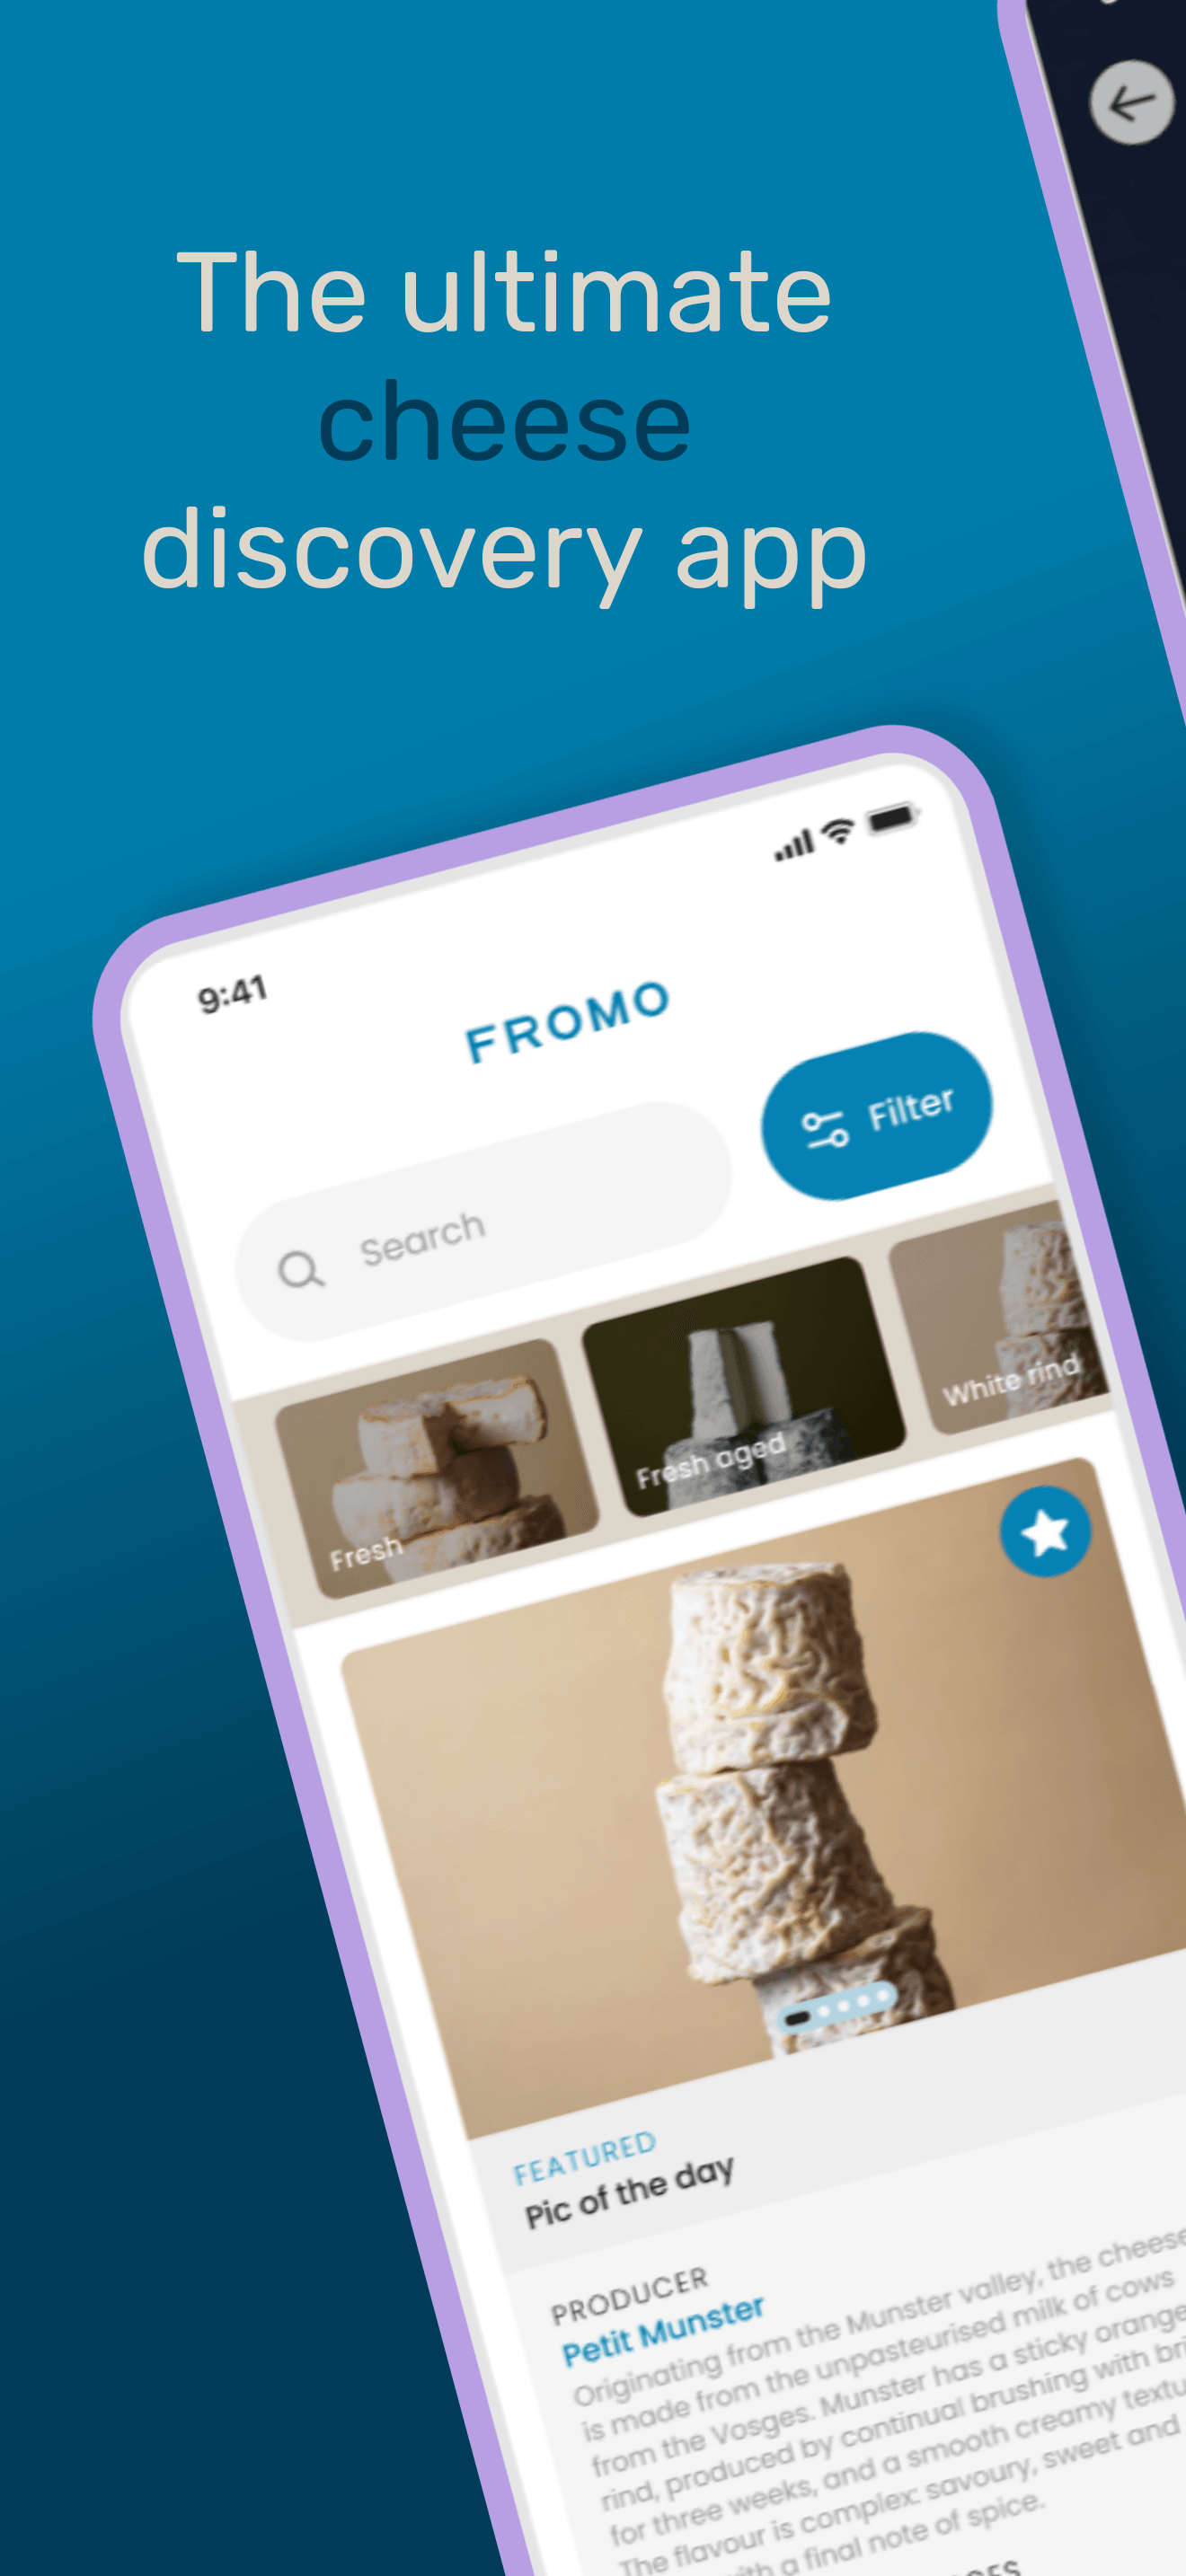
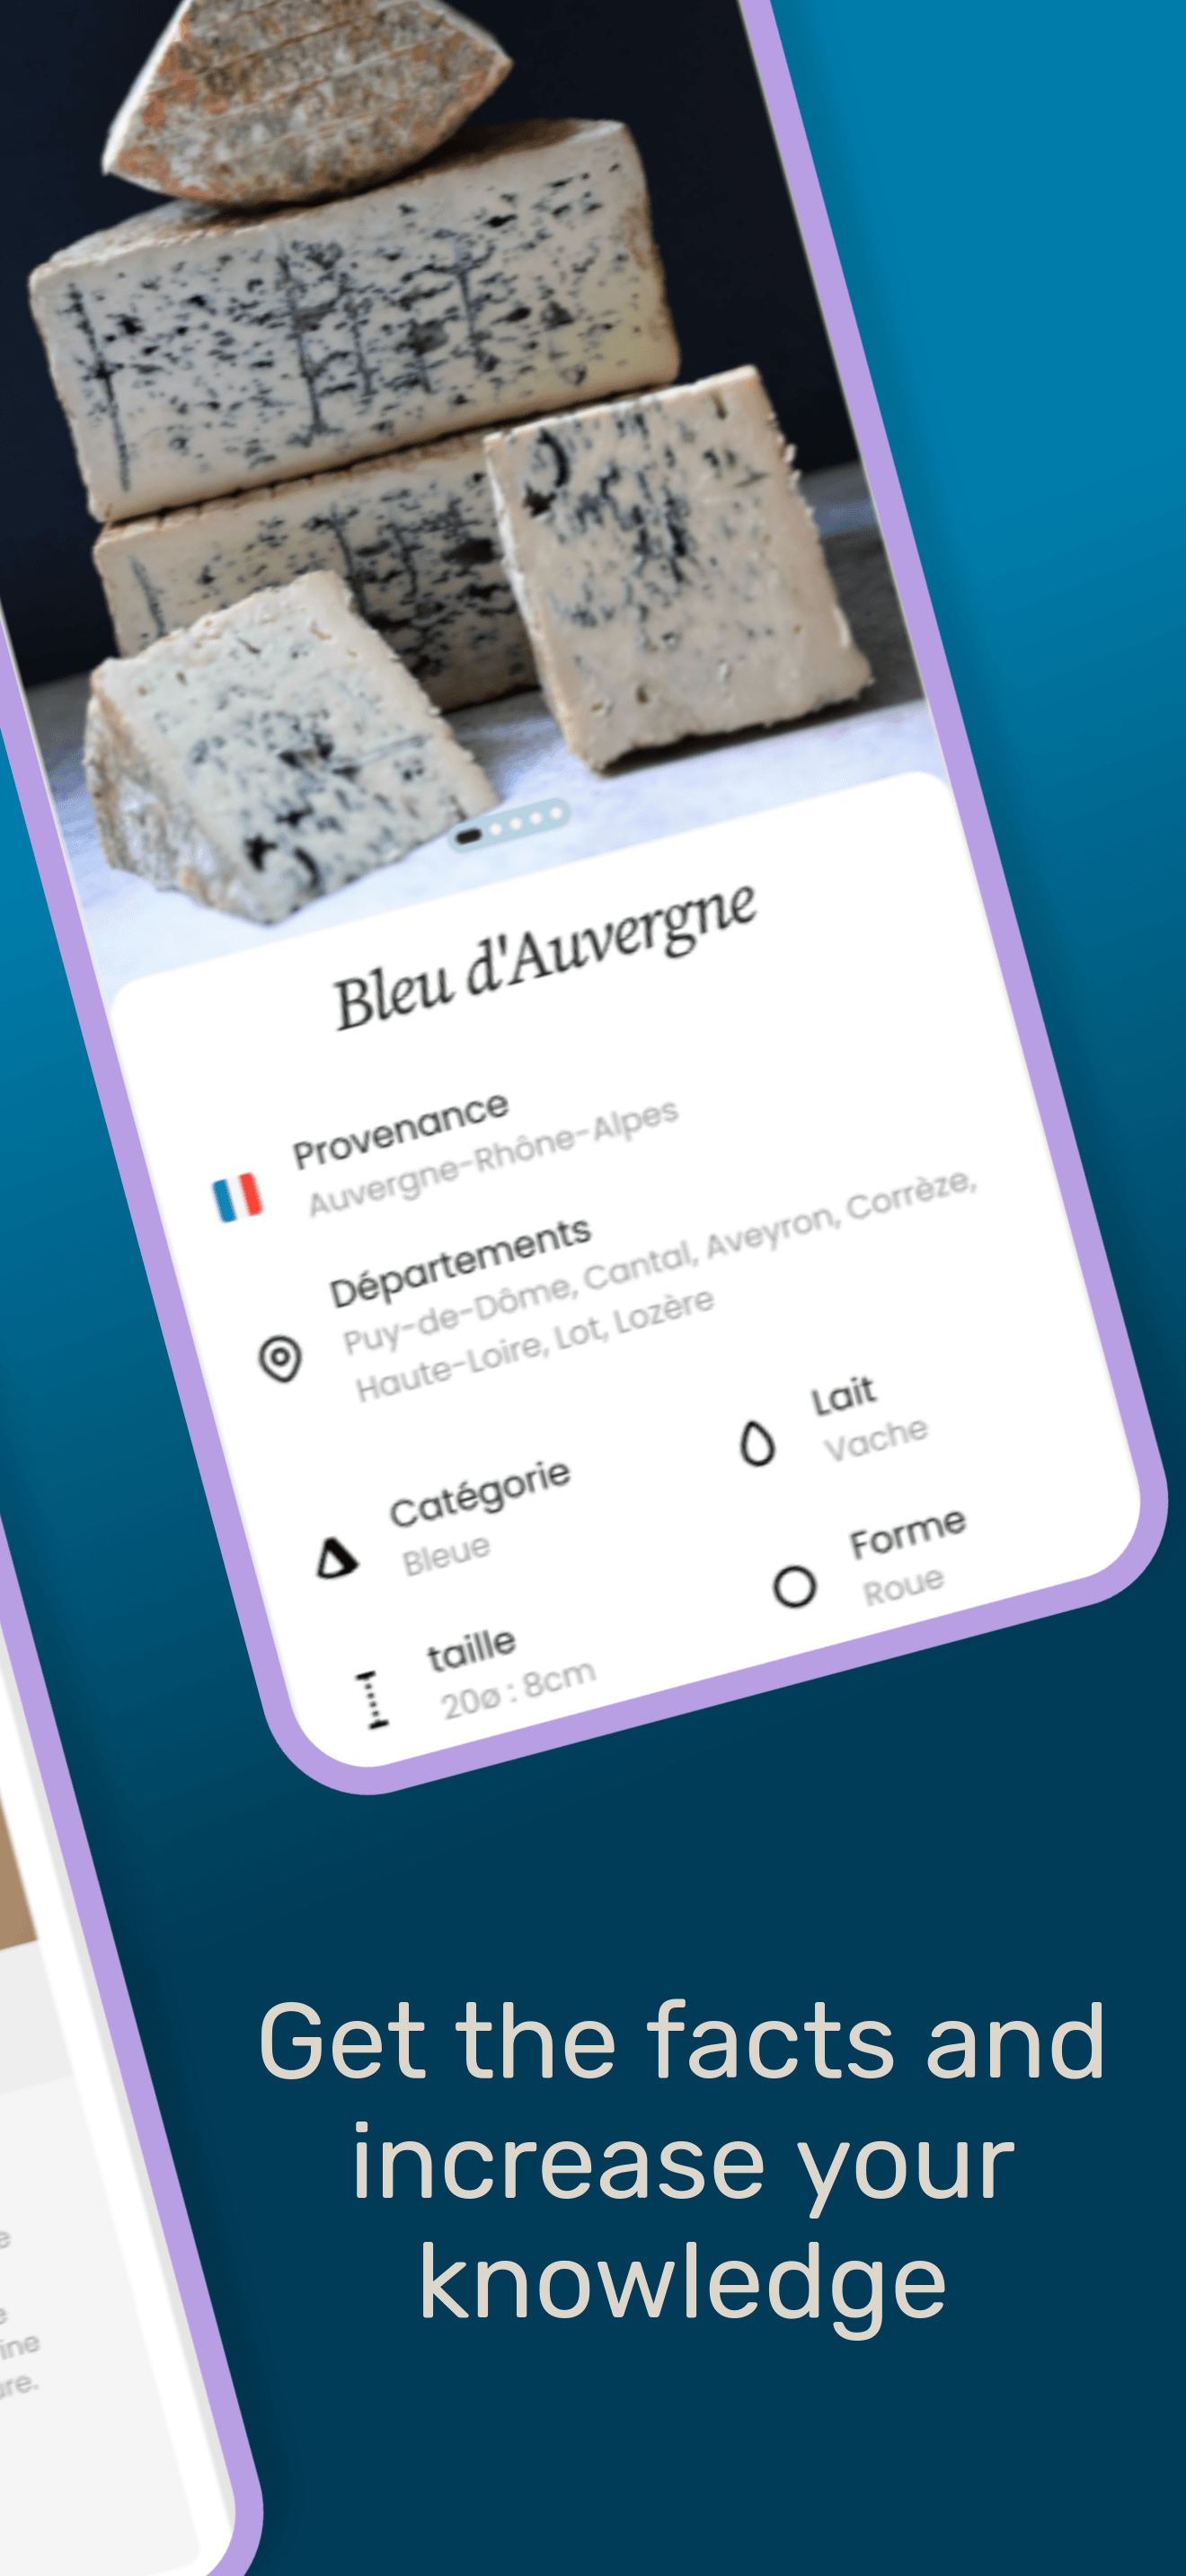
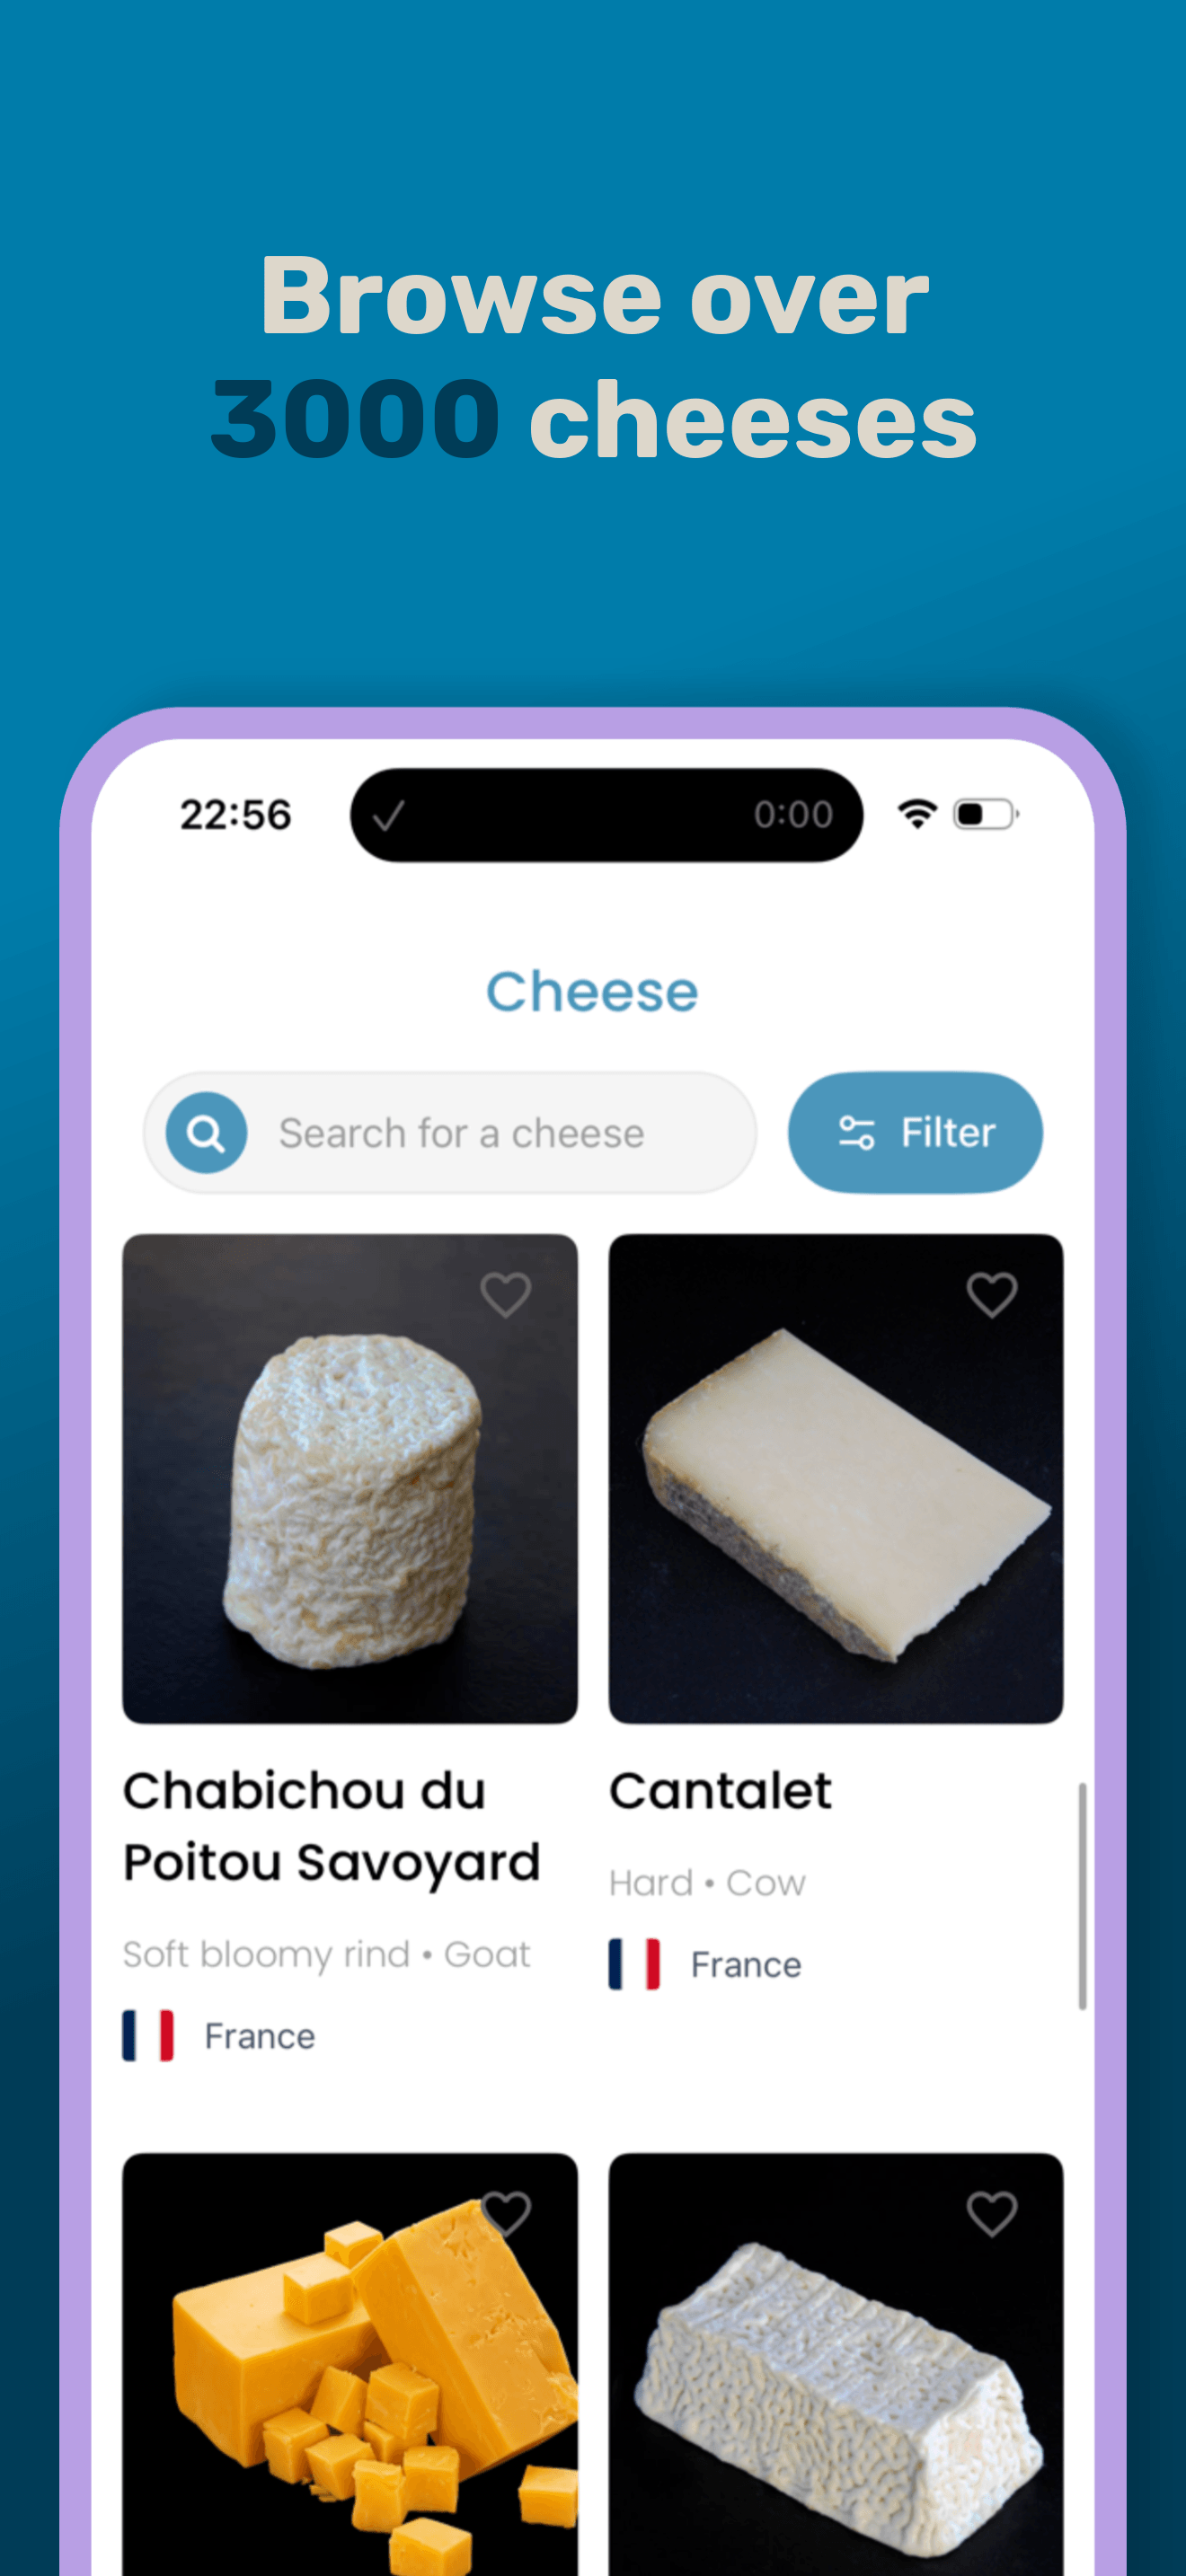
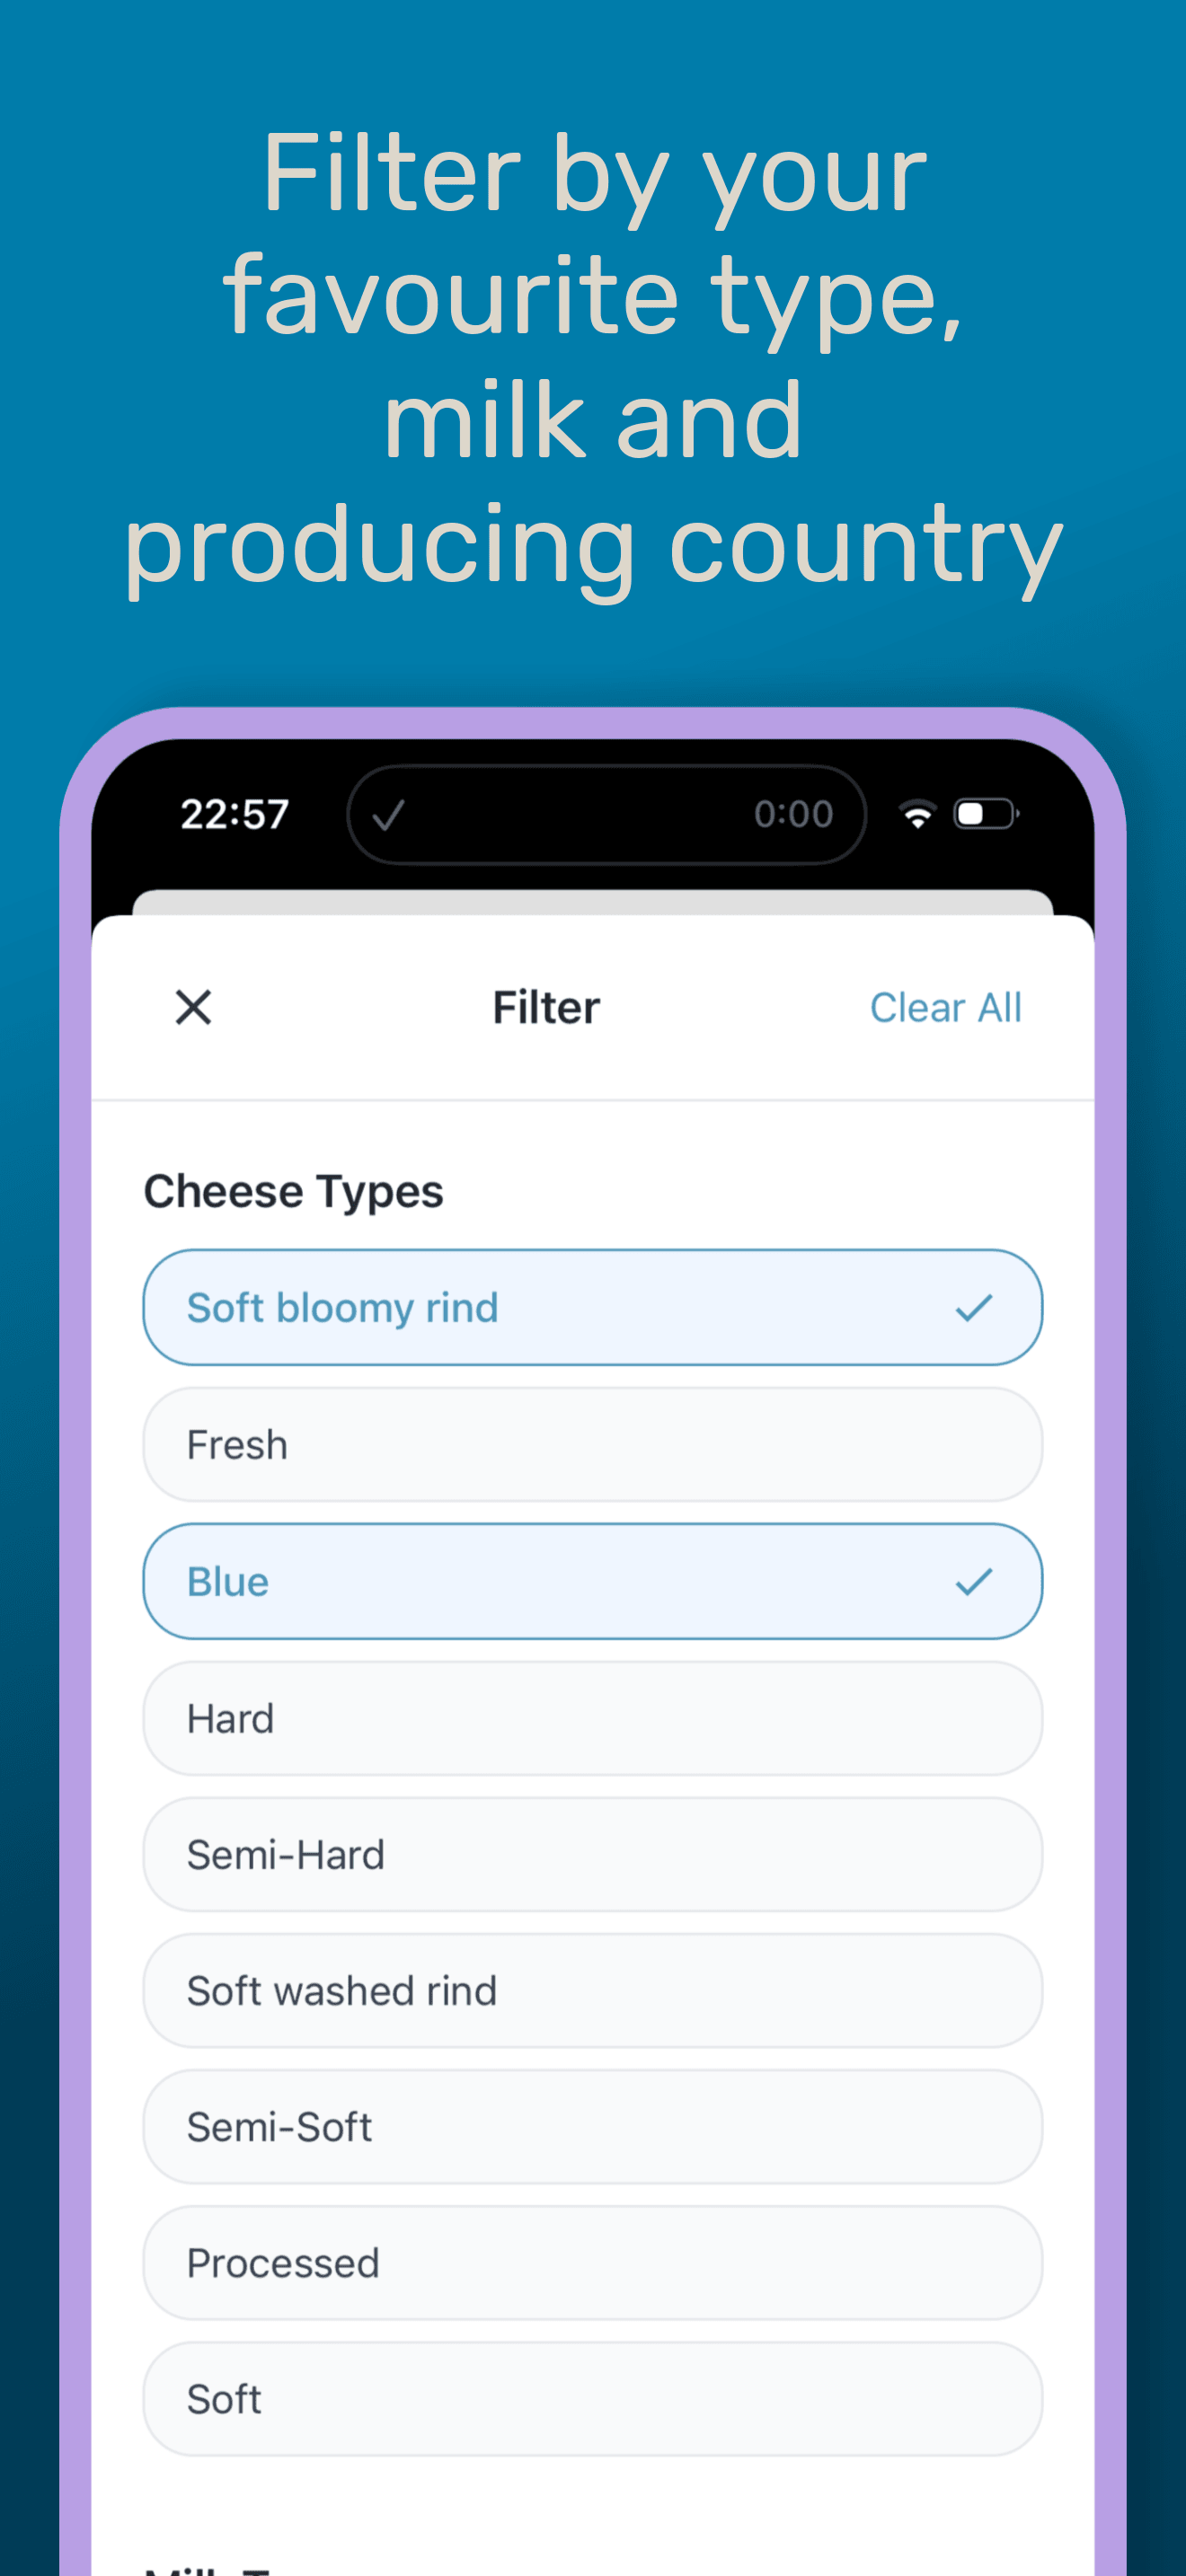
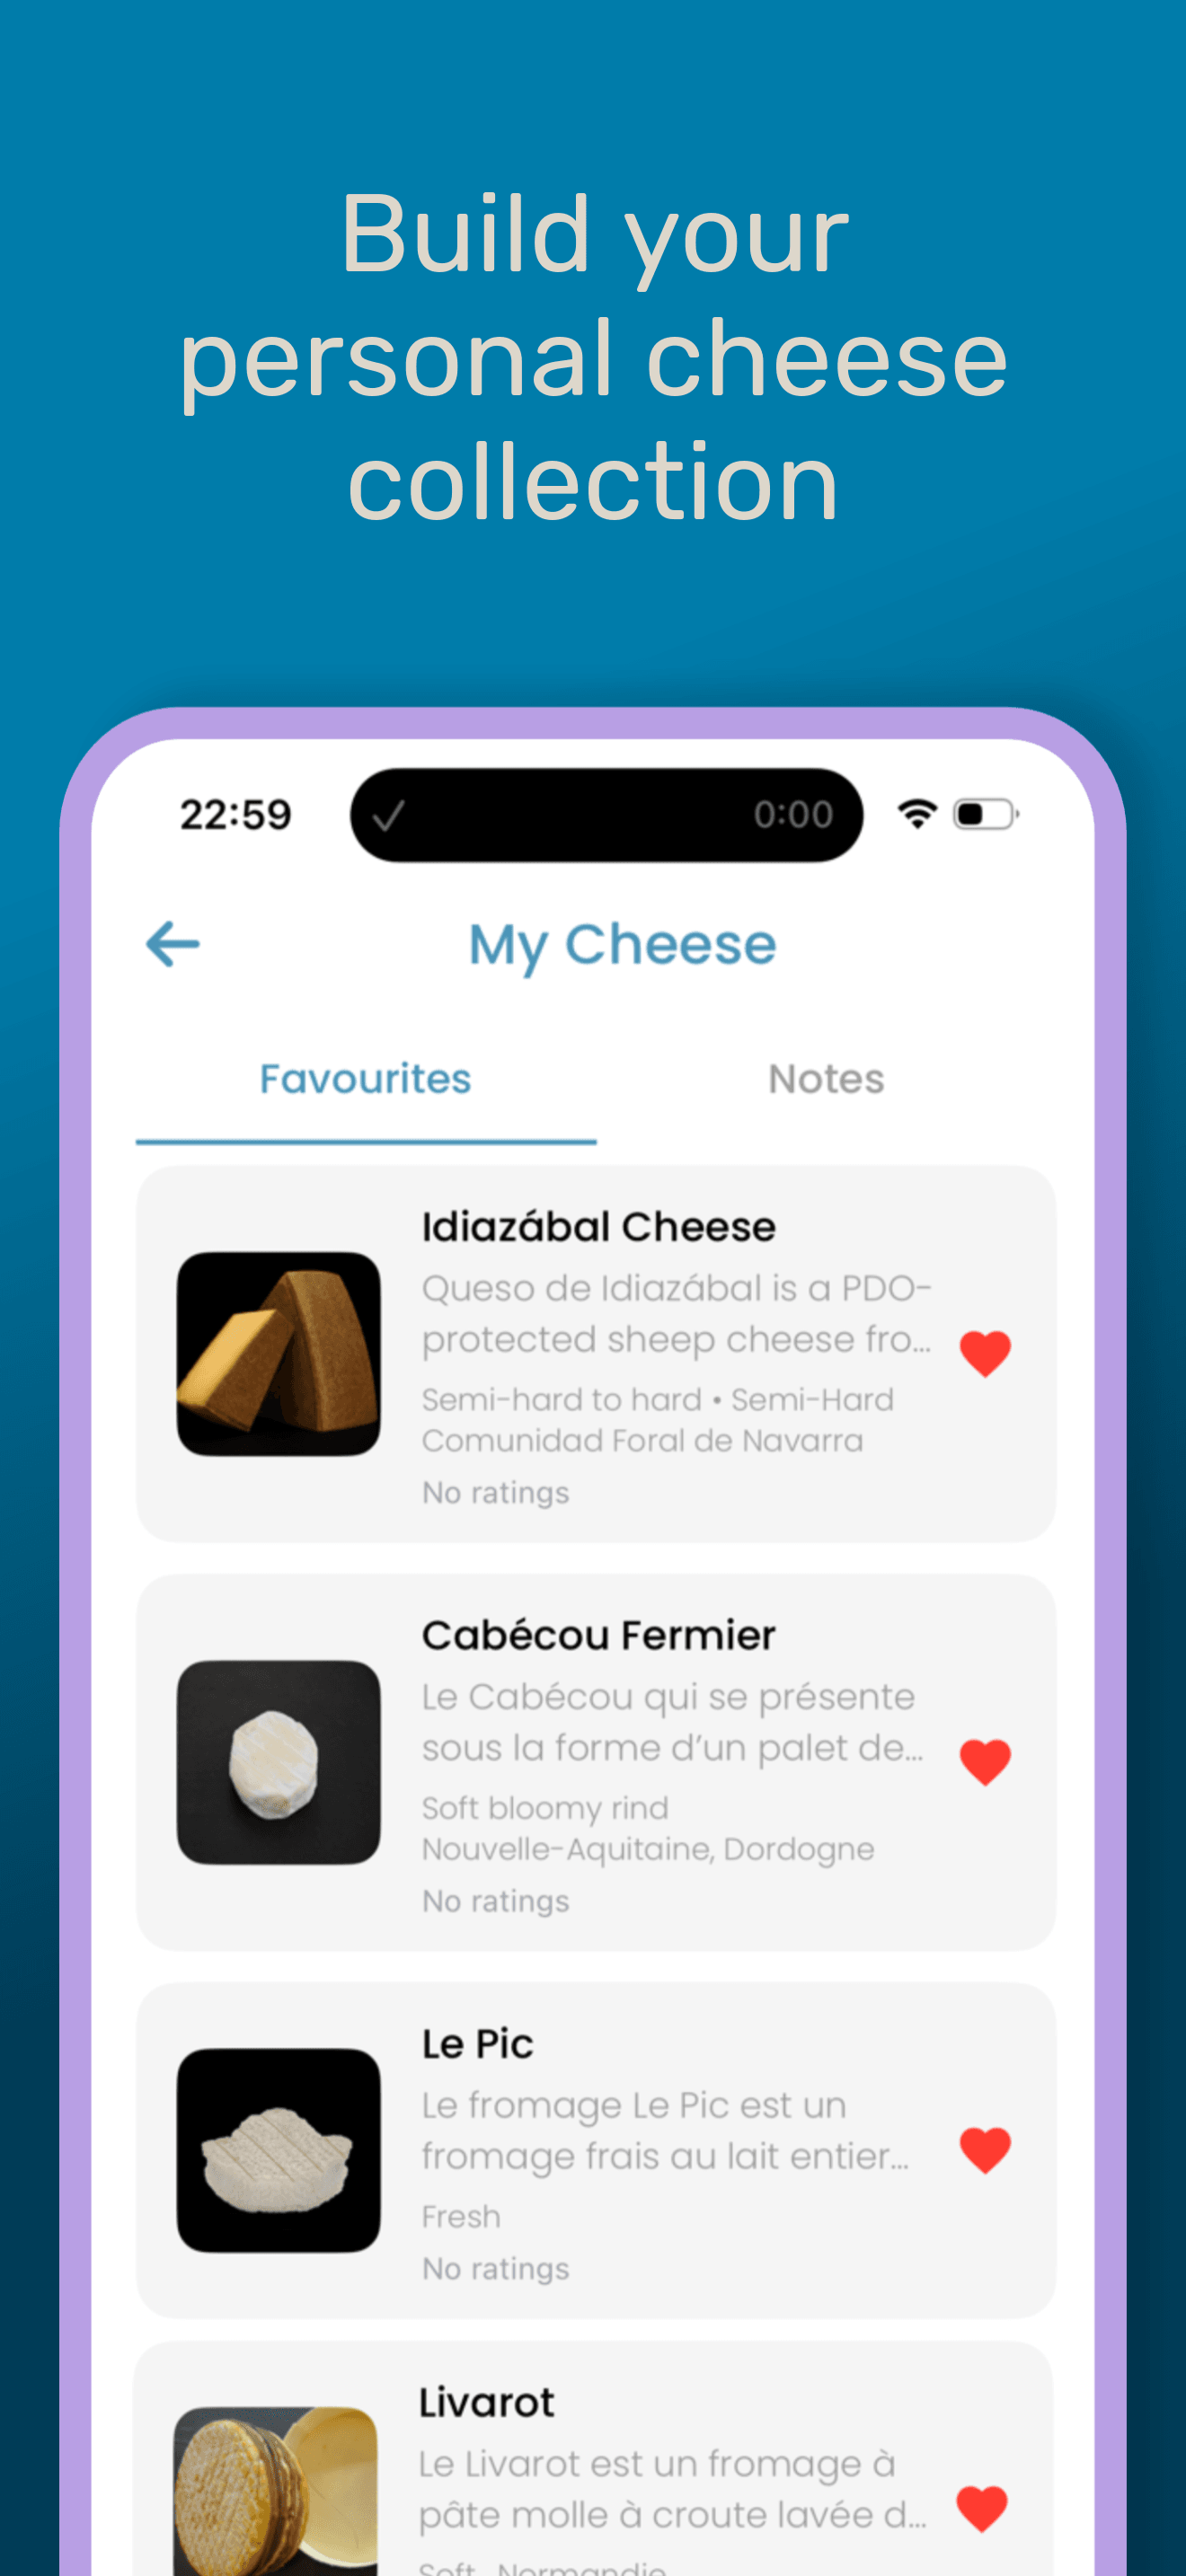
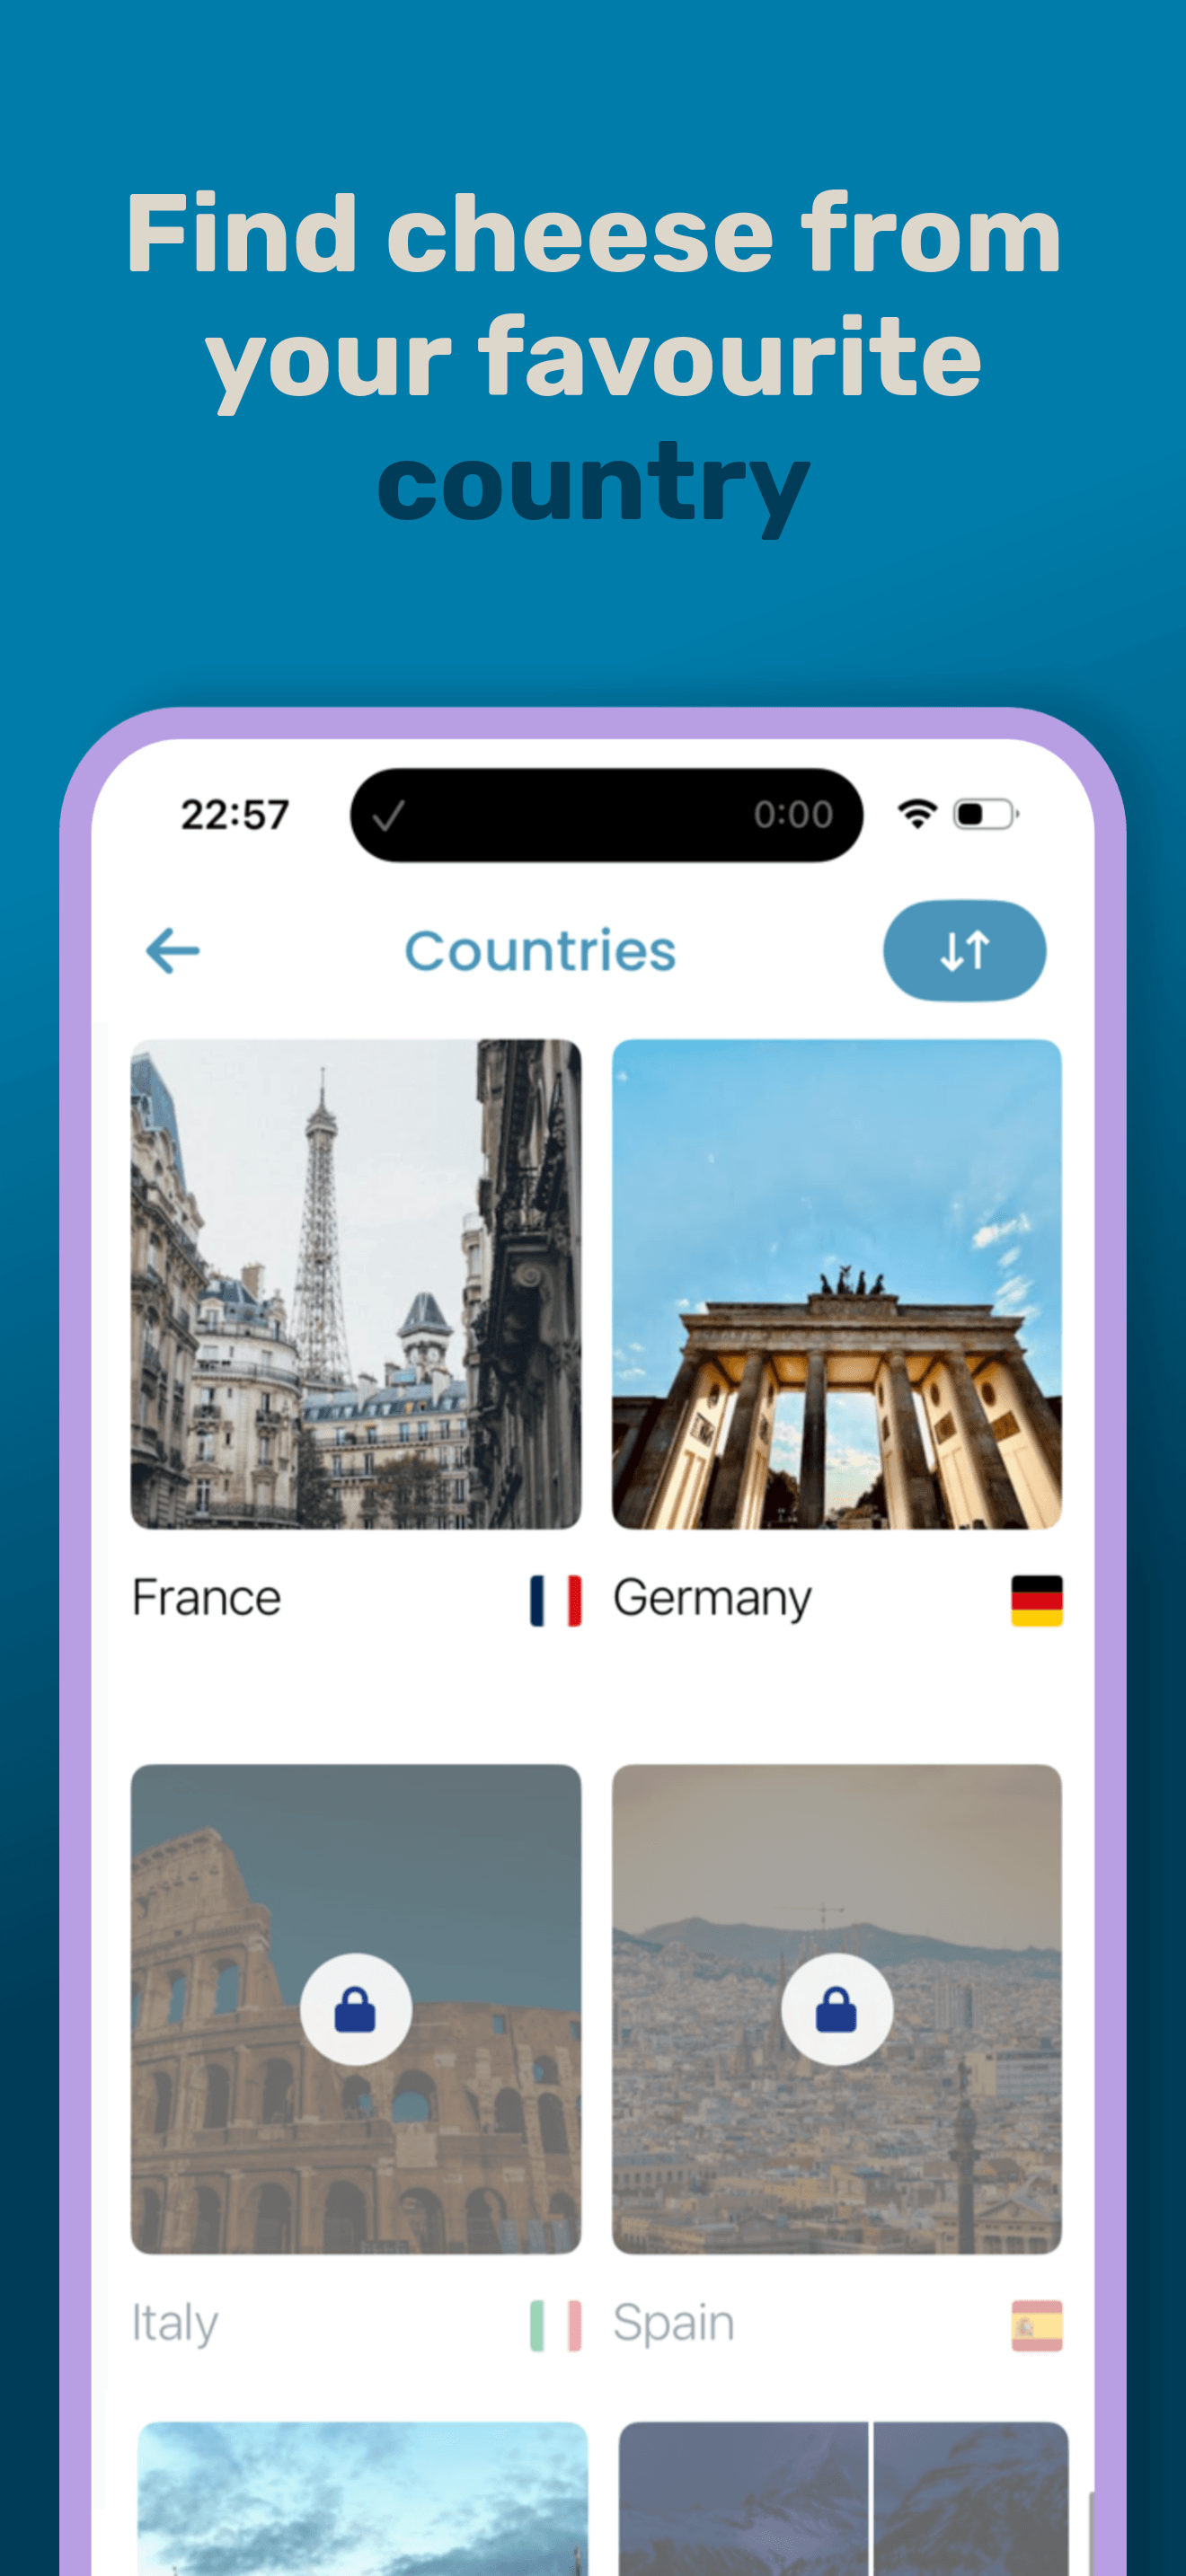
An iOS discovery app for cheese enthusiasts, covering a database of 3,000+ cheeses. We designed browsing, filtering by type/milk/country, favoriting, and a personal notes & collection feature, plus the store listing so people can actually find it.
Security review
CybersecurityFromo holds personal collections, notes, and account data on top of a 3,000-cheese catalogue. We reviewed the app, the API, and the servers behind it so a consumer product is not a soft target.
Server & API review
The backend that serves the catalogue and user data: hosts, endpoints, rate limits, and what is exposed without a session. Same full-server pass we run on larger products, sized to this stack.
Account & collection data
Favourites, notes, and collections scoped to the signed-in user. No shared or guessable object IDs leaking someone else's cellar.
Transport & sessions
TLS, token lifetime, and how the app stores credentials on device. Sessions that die when they should, not when the user remembers to log out.
Client hardening
ATS, keychain use, and the usual iOS footguns — debug leftovers, overly broad entitlements, and logs that should never include personal data.
More work under NDA
Internal tools we've shipped for clients aren't public. Happy to walk through them on a call.